New AI-Powered Infostealer Market Turns Infected Computers Into Searchable Victim Profiles
Hudson Rock, an Israeli firm that tracks password-stealing malware, has investigated a new cybercrime marketplace that uses AI to turn infected computers into searchable profiles. Each stolen log comes with an AI-written description of who the victim is, what they do, and what they might have access to.
According to Hudson Rock co-founder and CTO Alon Gal, the market marks a shift in the infostealer economy, “from selling stolen credentials to making entire digital lives searchable.”
The advertisement
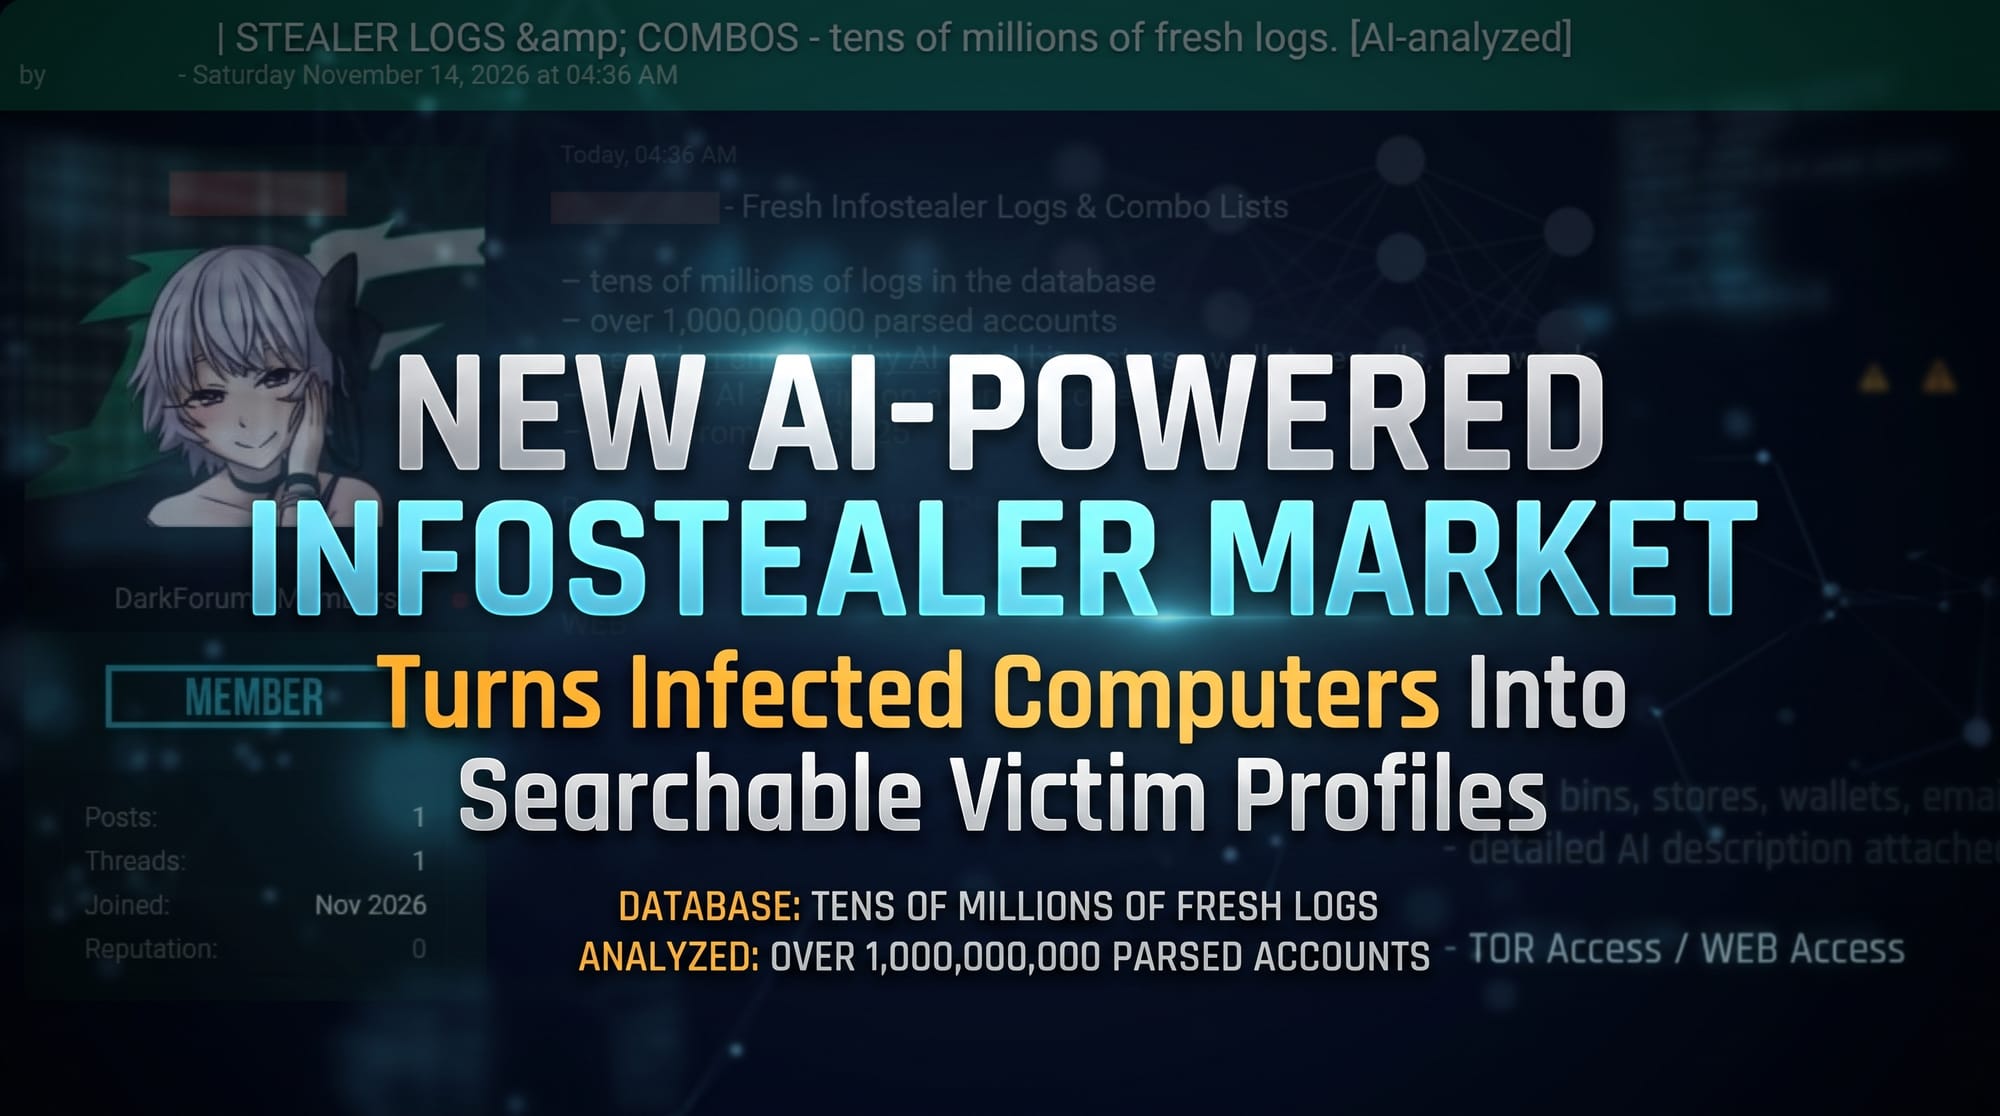
The service was advertised on cybercrime forums on November 14, 2026. A post on an underground forum titled “STEALER LOGS & COMBOS – tens of millions of fresh logs [AI-analyzed]” came from an account that joined in November 2026, with one post and no reputation. The seller claims:
- Tens of millions of logs in the database
- Over 1 billion parsed accounts
- Every log analyzed by AI for card BINs, stores, wallets, emails, and passwords
- A detailed AI description attached to each log
- Prices starting at $0.25
- Open, free registration, with access through both a web address and a Tor address
Hudson Rock treats these figures as the seller’s claims, not verified totals.
How it works
Buyers can type plain-English searches to find victims by job, employer, or the access their computer holds. They can also filter by country, operating system, price, and stealer family. The platform also has search modes by domain, mask, email, cookies, and files, plus a separate section for buying stolen accounts by domain.
Example listings
| Listing | Price | Details |
|---|---|---|
| Clinic front desk | $10 | A search for “citrix access to healthcare provider” returned a Canadian clinic workstation with Citrix VPN credentials |
| Government employee’s family computer | $10 | The listing claims it belongs to a Washington, D.C. government worker |
| AI researcher’s workstation | $10 | The seller claims it holds valid Claude API session tokens, which Hudson Rock has not verified |
| Defense contractor’s household | $9 | The listing mixes claimed corporate access with banking and gaming activity |
The clinic listing
The clinic listing, titled “The Ophthalmology Clinic Front Desk Dump,” describes a front-desk workstation at an ophthalmology clinic in a small Canadian city. According to the listing, it contains saved credentials for medical EMR systems, insurance claim portals, and billing software, along with access to a Citrix VPN that allows remote connection to the clinic’s infrastructure. The listing also says autofill data reveals multiple staff usernames and weak, predictable password patterns reused across accounts, and that an external IT provider manages the machine with remote monitoring tools installed.
Hudson Rock matched real victims
Hudson Rock matched several listings to records in its own database. In the clinic case, a unique Firefox profile ID in the listing matched a Canadian workstation labeled “Reception.” That computer’s files held Citrix login URLs and billing-related usernames.
Read the claims carefully
Hudson Rock cautions that:
- Saved passwords don’t prove a login or session still works.
- Job titles, tags, and scores are the seller’s marketing labels.
- A visit to an organization’s website doesn’t prove the victim works there.
- Domain listings for sites like fbi.gov don’t mean those organizations were breached. A domain search on the market also returned Uber accounts, and Hudson Rock says this does not mean either organization was breached.
What defenders should do
Hudson Rock recommends:
- Clean the infected machine before you reset anything.
- Reset exposed passwords from a trusted device.
- Revoke affected sessions and tokens.
- Review login and audit logs for unfamiliar sessions or account changes.