Your Eyes in the DarkYour Eyes in the Dark — Proactive Intelligence

Ransomware

The Gentlemen Ransomware Group Claims NVIDIA as Victim
1 min read

The Gentlemen ransomware group has added NVIDIA to its leak site.

The listing
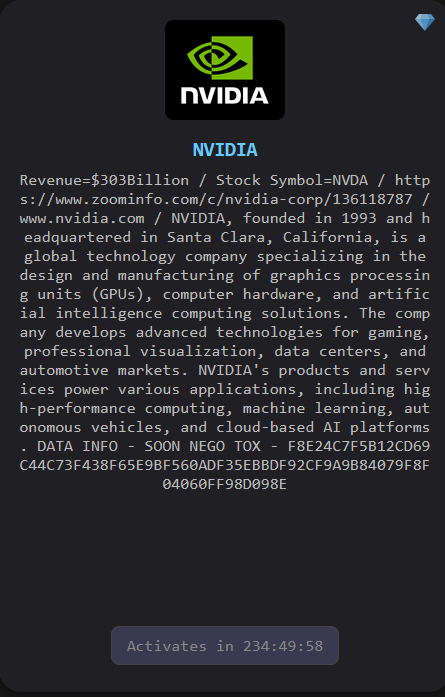
The group’s post describes NVIDIA as a global technology company founded in 1993 and headquartered in Santa Clara, California, specializing in graphics processing units (GPUs), computer hardware, and artificial intelligence computing solutions. The listing also cites a revenue figure of $303 billion and the stock symbol NVDA.
Status

DetailInformation
VictimNVIDIA
Threat actorThe Gentlemen
Data infoMarked “soon”
NegotiationTox ID provided for negotiation
CountdownActivates in about 234 hours

The group has not yet published details of the allegedly stolen data. The listing says data information is coming “soon” and includes a Tox ID for negotiation, with a countdown of about 234 hours until the listing activates.

The claim has not been independently verified, and NVIDIA has not publicly commented at the time of writing.

We will update this post as the countdown ends or NVIDIA responds.
Get the latest dark web news in your inbox

Ransomware, breaches and exploited vulnerabilities, from The Darkweb News.

Free. No spam. Unsubscribe in one click.

Latest news

Ruby Patches “Ruby2Shell” Vulnerability That Could Lead to Remote Code Execution

Zero-Day / Patch

Fresh security updates for the Ruby programming language fix seven vulnerabilities in its regular expression engine and in string case conversion. Proof-of-concept (PoC) code demonstrating remote code execution (RCE) exists for five of them. The main flaw: Ruby2Shell (CVE-2026-132825) The top vulnerability, CVE-2026-132825 (CVSS 7.4), is a heap-based buffer overflow in string case conversion that could lead to RCE in certain scenarios. It’s been dubbed Ruby2Shell. How it works The flaw affects

China-Linked Armory Castle Exploits VMware vCenter Zero-Day for Admin Access and Data Theft

Zero-Day / Threat Intelligence

The suspected China-nexus cyber espionage group Armory Castle (formerly UNC5221) has been attributed to the zero-day exploitation of a critical flaw in VMware vCenter Server, starting in early September 2026. The vulnerability Tracked as CVE-2026-123890 (CVSS 9.8), the flaw is an authentication bypass in the VMware Directory Service. According to Google Threat Intelligence Group and Mandiant, it’s an unauthenticated Secure Remote Password (SRP-6a) session key disclosure vulnerability over DCE/R

New Unpatched Windows Zero-Day Lets Someone Run Programs on a Locked PC

Zero-Day

A newly disclosed, unpatched zero-day technique called FastUnlock lets someone with physical access to a locked Windows computer start programs without signing in. Whoever uses it gets only a limited account, not administrator control of the machine. Who disclosed it The method was posted by a researcher using the handles MSNightmare and Nightmare Eclipse. Endpoint-security firm ThreatLocker tested it the same day and confirmed it works. There is no fix from Microsoft yet, and nothing shows the