root@ransomvault:~$ tail -f threat_intel.log

New N-able N-central Zero-Days “4EverAble2Shell” and “Agent2Shell” Bypass Able2Shell Hotfix; Exploitation Attempts Already Seen

Malware / Patch

N-able says it is investigating a new public disclosure of more vulnerabilities in on-premise N-central servers running version 2026.4.1 HF2. That is the hotfix it released only days ago to fix the Able2Shell vulnerabilities. Public proof-of-concept (PoC) exploits are available, and threat intelligence firms have already seen targeted probing within hours of their release. Background: Able2Shell Earlier this week, independent security researcher Sean Bales disclosed several security flaws in N-
Critical Red Hat Quay Flaw Lets Attackers Take Over Registry Token Signing

Vulnerability / Patch

Red Hat has disclosed a critical vulnerability in Red Hat Quay, its enterprise container registry for storing, managing, and distributing container images. The flaw is tracked as CVE-2026-123710 and has a CVSS 3.1 score of 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). It lets an attacker take over registry token signing and gain full read and write access to every repository in the registry. How the attack works The flaw is in Quay’s service key server, the component that manages signing

Former FBI Supervisor Pleads Guilty to Stealing $2.47 Million in Cryptocurrency from FBI Investigations

Threat Intelligence

Patrick Steven Yaroch, a 37-year-old former FBI supervisor, has pleaded guilty to wire fraud and money laundering. He stole about $2.47 million in cryptocurrency from wallets linked to FBI investigations. He entered the guilty plea on November 5, 2026, according to the U.S. Department of Justice (DOJ). How the theft worked According to the FBI’s search affidavit, Yaroch accessed FBI systems that stored the seed phrases of cryptocurrency wallets belonging to investigation subjects, and memorized

Maersk Confirms Security Incident Following Whitearmor’s Claimed Breach of LF Logistics Platform

Ransomware

A.P. Moller - Maersk has confirmed an IT security incident. The confirmation came shortly after we reported that the Whitearmor threat group claimed to have breached Maersk’s LF Logistics platform. What Maersk confirmed In a statement published on November 11, 2026, Maersk said it had found unauthorized access to, and data extraction from, one of its local legacy systems that came from a previous acquisition. Maersk did not name the system or the threat actor. However, the description matches L

Node.js Fixes 16 Vulnerabilities, Including HTTP/2 Crash and HTTPS Memory Leak That Can Expose TLS Private Keys

Vulnerability / Patch

The Node.js project has released security updates that fix 16 vulnerabilities in the runtime, seven of them rated high. The most serious flaws are in Node.js’s built-in HTTP/2, HTTPS, and TLS server code. They let unauthenticated clients crash servers, corrupt memory, or read memory from other connections, which can include TLS private keys and other users’ requests. Fixed versions are available for all three supported release lines: 22.23.5, 24.22.3, and 26.13.1. HTTP/2 crash (CVE-2026-123863)

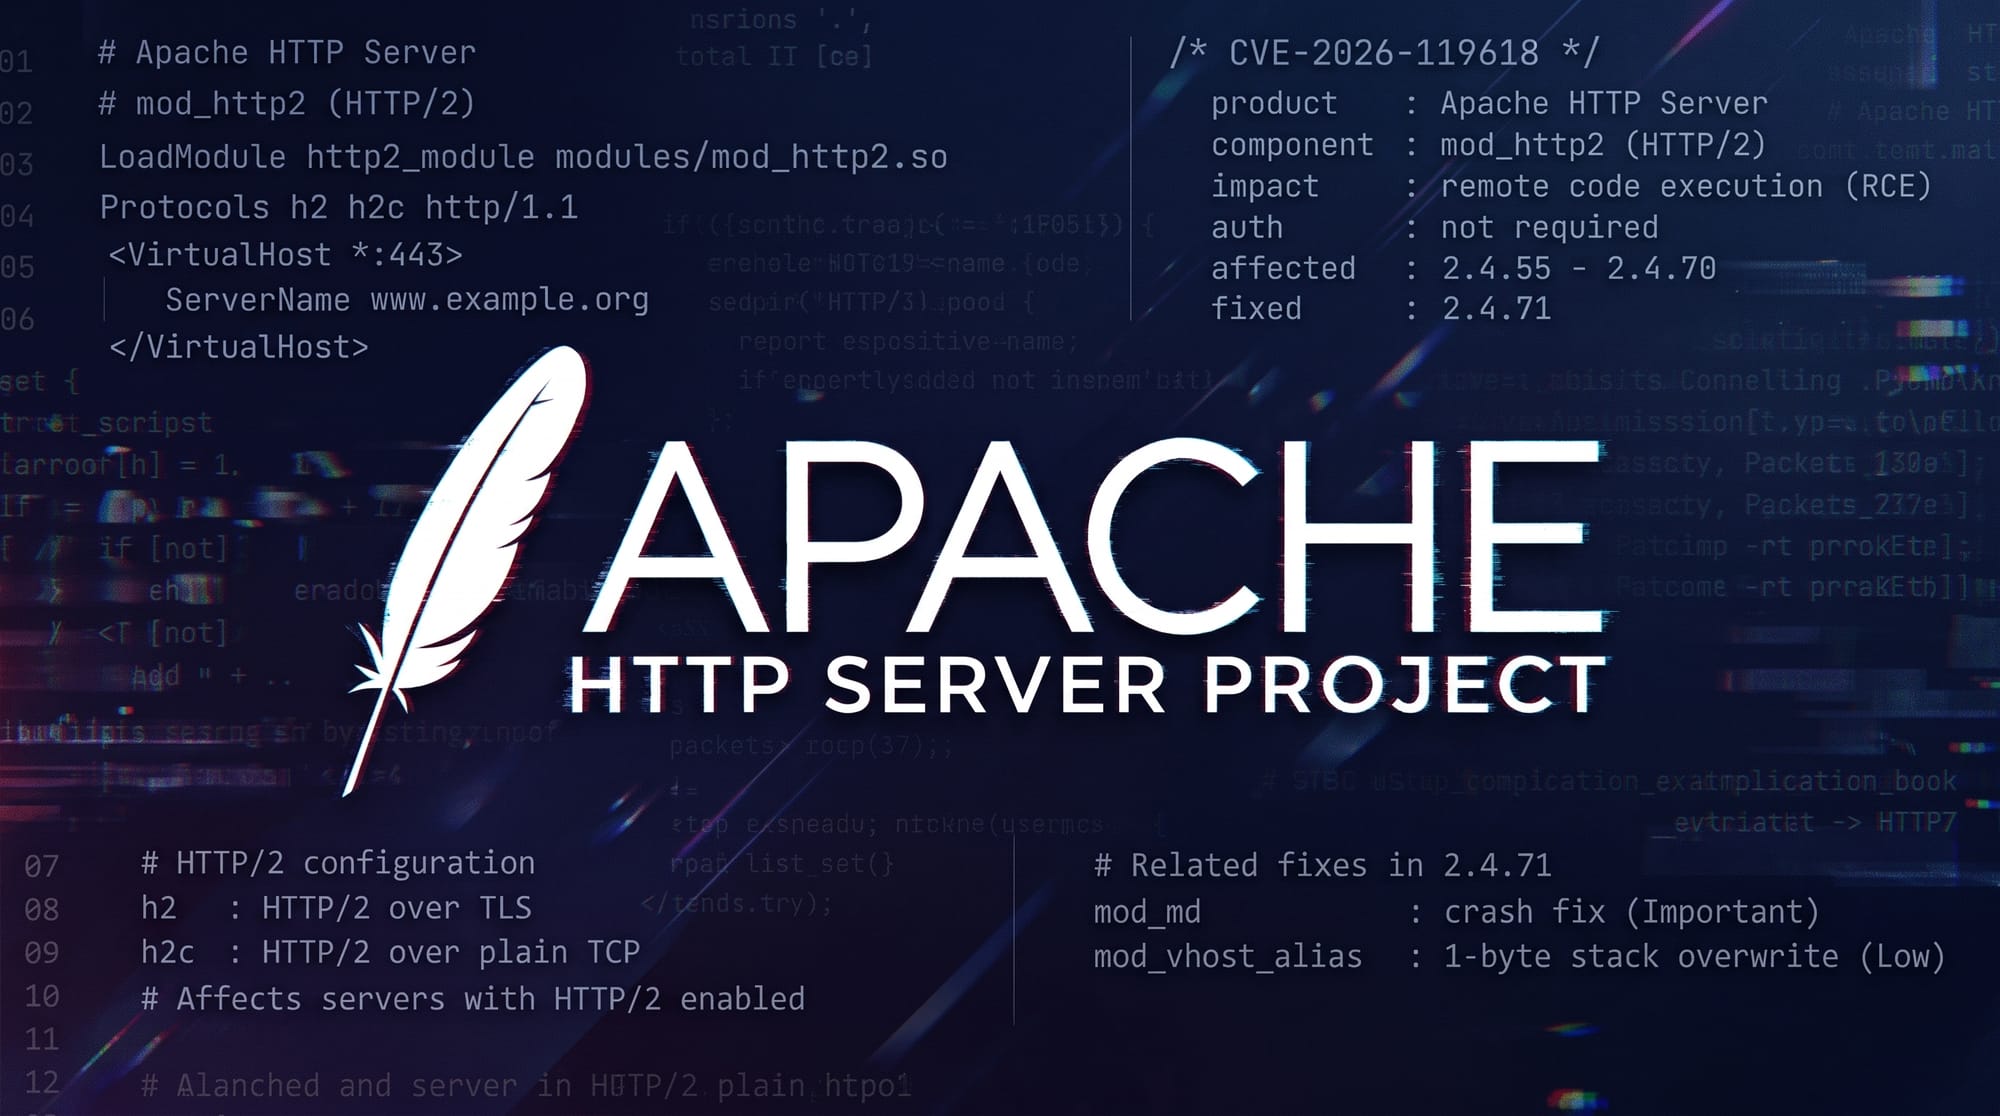
Critical Apache HTTP Server Flaw in mod_http2 Enables Unauthenticated Remote Code Execution

Vulnerability / Patch

A critical vulnerability in Apache HTTP Server’s HTTP/2 module, mod_http2, could let a remote attacker run code on vulnerable servers. The flaw is tracked as CVE-2026-119618 and rated 9.8 on the CVSS scale. It affects Apache HTTP Server versions 2.4.55 through 2.4.70 and is fixed in the newly released version 2.4.71. Who is affected Only servers with HTTP/2 enabled are vulnerable. HTTP/2 is turned on with the Protocols directive: h2 enables HTTP/2 over TLS, and h2c enables HTTP/2 over plain TCP

Zoom Patches Critical Privilege Escalation Flaws in Zoom Workplace for Windows

Vulnerability / Patch

Zoom has released security updates for two vulnerabilities in Zoom Workplace for Windows. One of them is rated critical. Both let an unauthenticated attacker escalate privileges over the network, with no special permissions or prior access needed. The vulnerabilities * CVE-2026-108186 (CVSS 9.6, Critical): An improper input validation flaw. An unauthenticated user with network access could exploit it to escalate privileges. It affects Zoom Workplace for Windows from version 7.1.0 up to, but n

Akira Group Leaks 30GB of Data Allegedly Stolen from Pelham Plastics November 11, 2026

Ransomware

Akira ransomware group has listed Pelham Plastics on its data leak site. Pelham Plastics is a custom plastic engineering company that makes injection molds and custom equipment, mainly for medical applications. The listing was posted on November 11, 2026. What the group claims The group says it stole about 30GB of corporate data, including: * Employee personal information, including passport and driver’s license scans * Confidential internal files * Contracts and agreements * Client inform

BYOD Ransomware Group Claims Breach of Toyota

Ransomware

The BYOD ransomware group has added Toyota to its data leak site. The post is marked “PSA” and was last updated on November 10, 2026. According to the listing, the stolen data includes: * Full names * Email addresses * Physical addresses * Phone numbers * Dates of birth * Kiosk device data In an unusual remark, the group says that “a lot was actually isolated.” This suggests Toyota’s defenses contained much of the intrusion, but the attackers claim they found “a few cracks” to get thro

Critical Fortinet2Shell Vulnerability

Vulnerability / Patch

Fortinet has warned about a critical flaw in FortiClient that lets a remote attacker run code on a user’s computer. The attacker only needs the user to visit a malicious website. The bug is tracked as CVE-2026-121529 and carries a CVSS score of 9.1. Fortinet published the advisory on November 10, 2026. The issue is an origin validation error, classified as CWE-346. Researcher Kevin Joensen from Baldur Security discovered it during internal research and humorously dubbed it “Fortinet2Shell.” He